Cyber risk can be difficult to assess when systems, processes and responsibilities are spread across different teams. Many organisations know cyber threats exist but struggle to understand where their biggest risks sit, what requires attention first and how to prioritise action.
A Cyber Risk Assessment is a structured review of your organisation’s exposure to cyber threats across people, processes and technology. It helps you understand your current cyber risk position, identify priority risks and develop a practical plan to reduce exposure, strengthen resilience and support better decision-making.
Many cyber incidents are linked to preventable issues such as human error, process gaps, outdated controls or unclear accountability. When these risks are not understood, organisations can be left exposed to operational disruption, data loss, compliance challenges and costly recovery efforts.
A Cyber Risk Assessment provides a clear picture of your organisation’s cyber risk environment so you can make informed decisions on what actions to prioritise.
Our Cyber Risk Assessment service helps organisations understand their exposure to cyber threats and develop a practical pathway for reducing risk. The outcome is a clear Cyber Risk Management Plan (CRMP) that aligns with your organisation’s operating environment, priorities and level of cyber maturity.
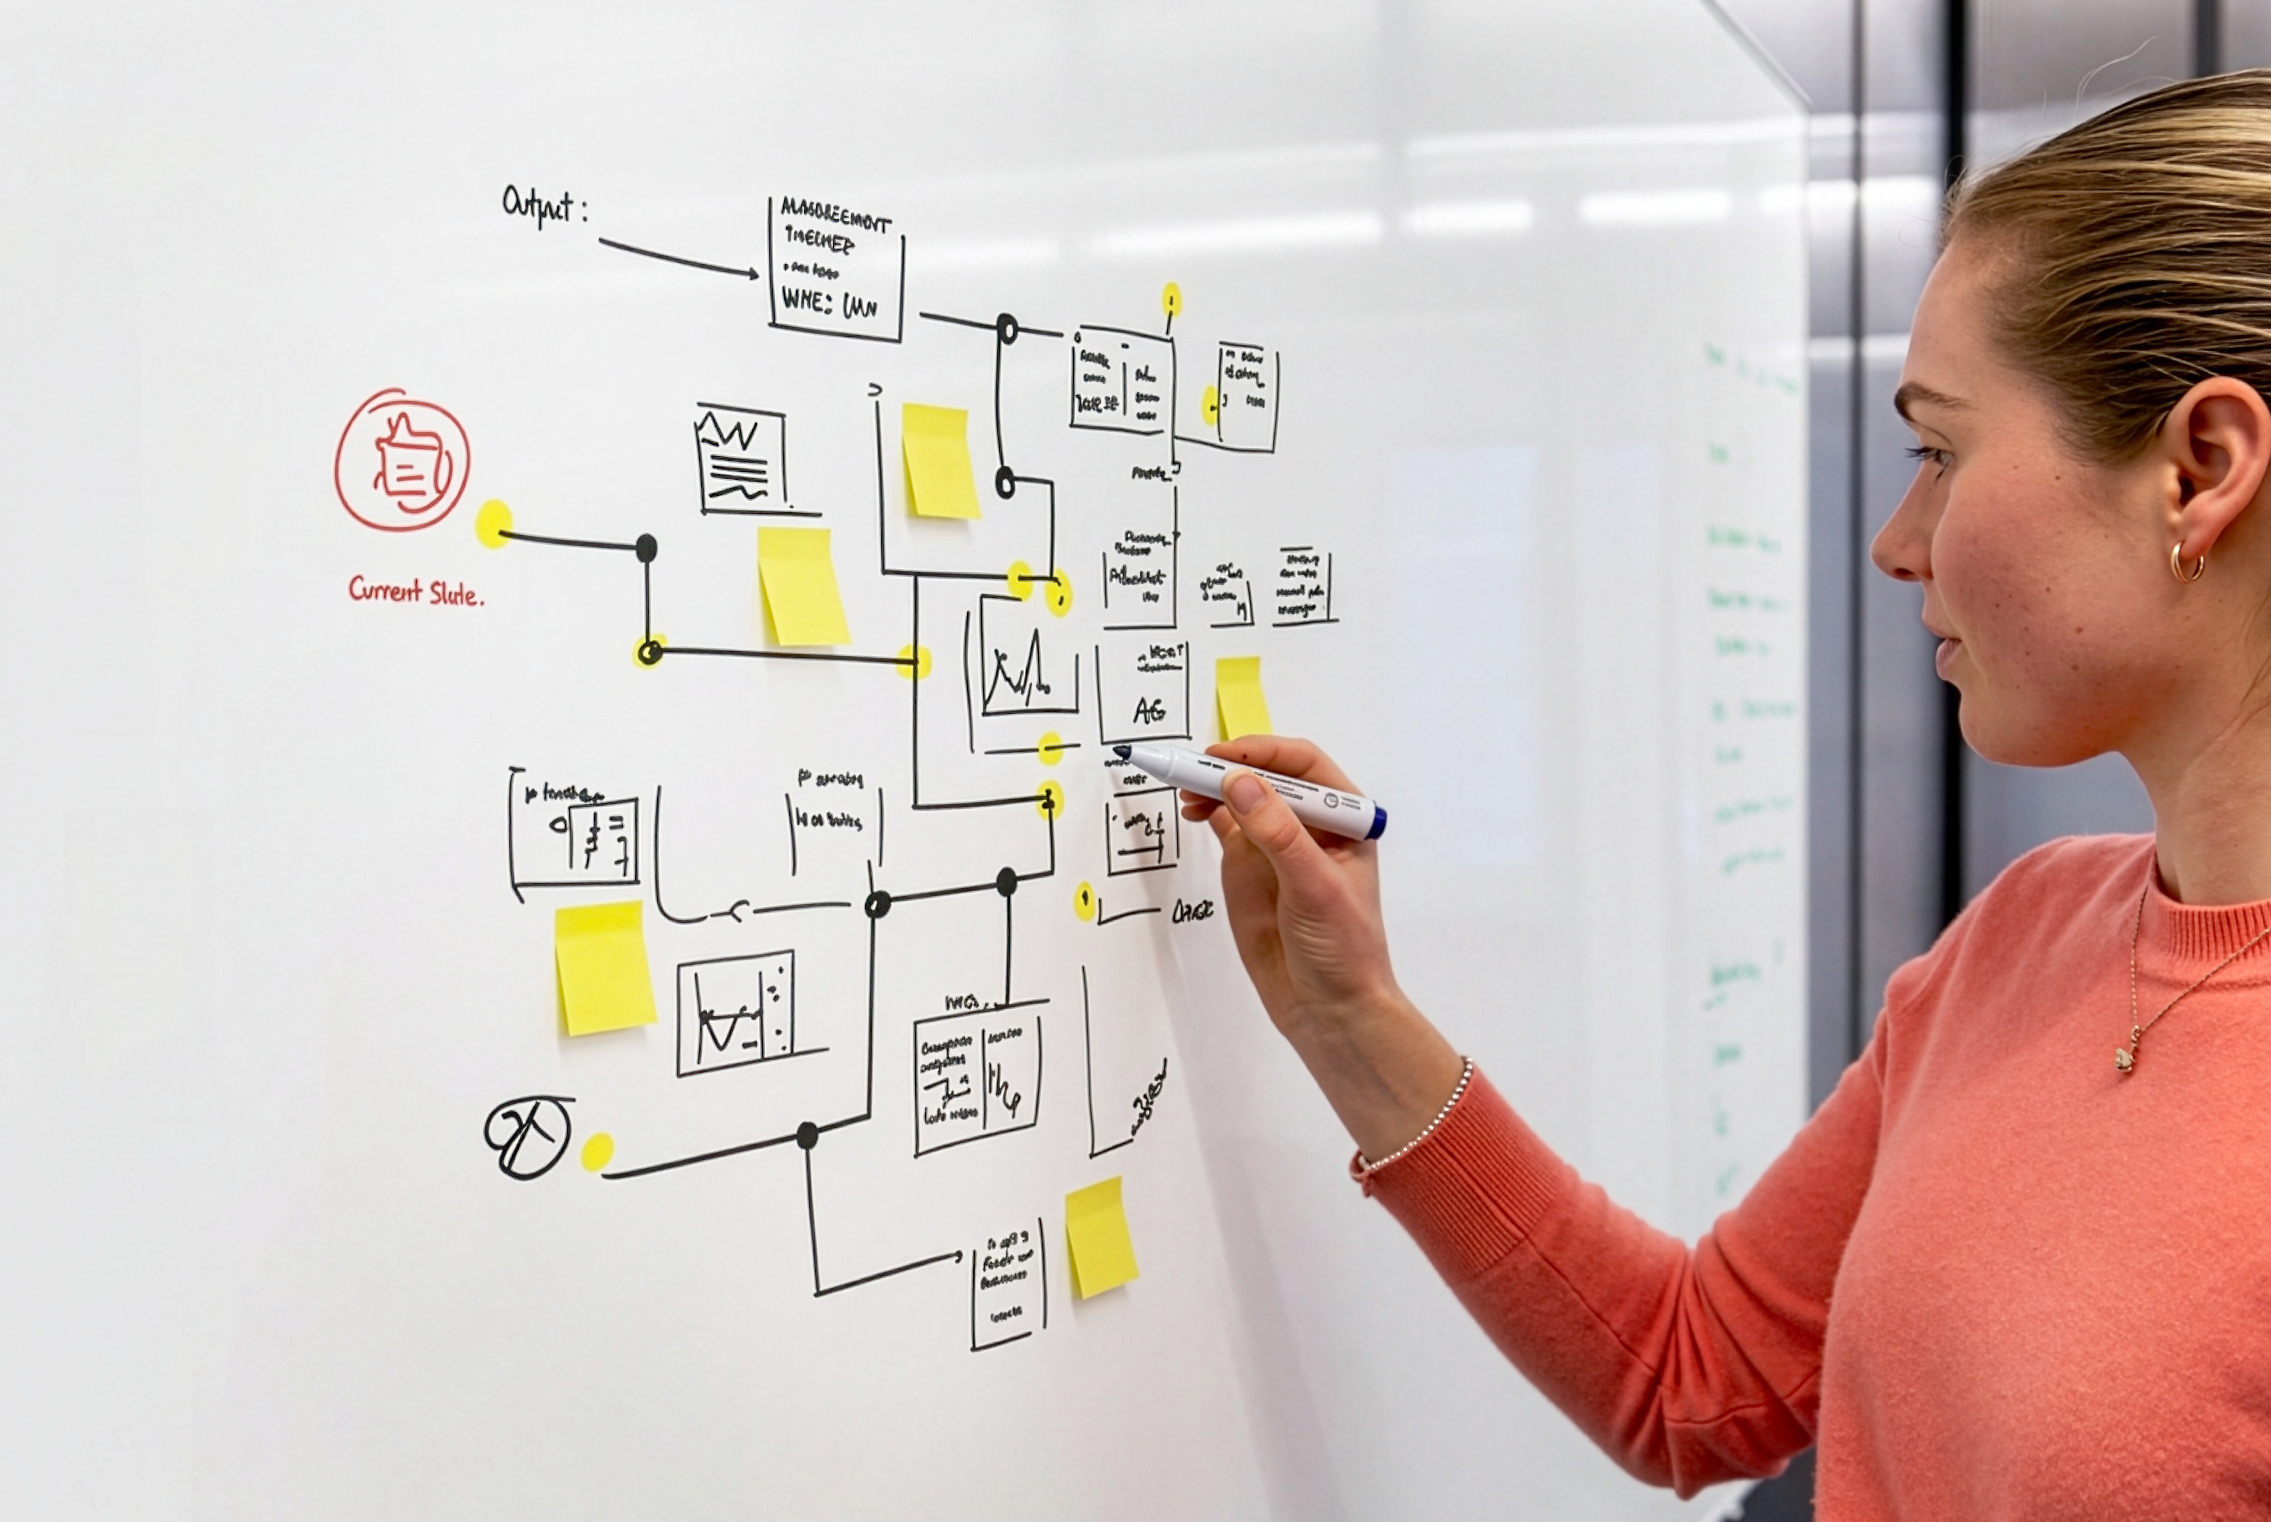
We work alongside your team to understand how people, processes and technology interact across your organisation. Using this information, we identify areas of exposure and develop recommendations that are practical, achievable and relevant to your context.
We begin with a tailored discovery process to understand your organisation’s systems, processes and ways of working. This helps us assess cyber risk within the reality of your operating environment rather than against a generic checklist.
We review the factors that influence cyber risk across your organisation, including behaviours, controls, technology and operational processes. This creates a balanced view of where exposure may exist and where improvements are needed.
We identify cyber risks relevant to your organisation’s size, industry, regulatory environment and strategic objectives. Recommendations are prioritised based on risk level, impact and practicality, helping your team focus on what matters most.
We translate findings into a Cyber Risk Management Plan supported by a clear Now – Next – Later roadmap. This provides a structured approach for reducing risk over time and helps decision-makers understand where effort should be focused first.
This service is ideal when your organisation needs to better understand its exposure to cyber threats and develop a practical, prioritised plan for reducing risk.
This service is valuable when your organisation needs a clearer understanding of cyber exposure, is preparing for growth or change, or requires greater confidence in risk-related decision-making.
It is also useful when cyber risk responsibilities are unclear, leadership teams need better visibility of risk, or existing cyber security efforts lack a clear plan and prioritisation framework.
Whether you're seeking a clearer understanding of cyber risk, preparing for organisational change or looking to prioritise risk reduction efforts, we can help. Get in touch to explore your current risk profile and develop a practical plan for reducing exposure over time.